Scaling IT and Enterprise Growth: A Conversation with Subir Sangal, CEO of Eagle Information Systems
Technology is changing faster than ever. AI, cloud computing, cybersecurity, automation, and digital transformation are creating new opportunities for businesses every day. But behind every successful technology company is a much bigger challenge: building a business that can adapt, earn customer trust, and continue growing in a constantly changing market. For technology entrepreneurs, having strong technical knowledge is only one part of the journey. The ability to understand customers, build the right team, make business decisions, and respond to changing market needs can be equally important. This is where the experience of leaders who have spent decades in the technology industry becomes particularly valuable. In a recent interview with Sugermint, Subir Sangal, CEO of Eagle Information Systems, shares his perspective on technology, entrepreneurship, cybersecurity, and the changing business landscape. His journey offers practical insights into what it takes to build and sustain a technology business in India. From Technology Expertise to Business Leadership Many technology founders begin their journey with a strong technical background. They know how to build products, solve complex problems, and understand technology at a deeper level. However, turning that technical expertise into a successful business requires a different set of skills, including sales, marketing, leadership, hiring, and understanding customer expectations. Subir Sangal’s entrepreneurial journey provides an interesting perspective on this transition. Over the years, he has witnessed significant changes in the technology industry and the way businesses use technology to solve real-world problems. His experience highlights why successful technology leadership is not just about keeping up with new technologies but also about understanding how those technologies create business value. His interview also gives readers an opportunity to look beyond the usual startup success stories. It explores the lessons, challenges, and decisions that shape a technology entrepreneur’s journey. For anyone interested in entrepreneurship or the Indian technology sector, these insights offer plenty to think about. Why Technical Founders Need More Than Technical Skills A great product does not automatically become a successful business. A founder may build an excellent technology solution, but if they cannot communicate its value, reach the right customers, or create a strong team around it, growth can become difficult. This gap between technical capability and business capability is one of the challenges many technology entrepreneurs face. The technology industry has seen several examples where strong technical ideas struggled because the business side was not given equal attention. Understanding pricing, sales, marketing, hiring, and leadership can make a significant difference in turning an idea into a sustainable company. In his conversation with Sugermint, Subir Sangal discusses this broader side of entrepreneurship through examples and experiences from the technology world. His observations make the interview particularly relevant for founders who are trying to move from being technology experts to becoming well-rounded business leaders. Cybersecurity Is No Longer Just an IT Concern As businesses become increasingly dependent on digital systems, cybersecurity has moved from being a technical issue to a business priority. A cyberattack can affect operations, customer trust, financial performance, and even a company’s reputation. This makes cybersecurity an important consideration for businesses of every size. For small and medium-sized businesses in particular, the assumption that cybercriminals only target large organizations can be dangerous. Automated attacks and constantly evolving threats mean that businesses need to think about security proactively rather than waiting for an incident to happen. The interview provides an opportunity to understand how an experienced technology leader views this changing cybersecurity environment. It also highlights the importance of building awareness and taking security seriously as businesses continue to adopt new technologies and digital platforms. What Can Entrepreneurs Learn From Subir Sangal’s Journey? One of the most interesting aspects of an entrepreneurial journey is that it is rarely a straight line. Businesses evolve, markets change and leaders are constantly required to make decisions with incomplete information. The ability to learn from these experiences often becomes as important as the original business idea. Subir Sangal’s experience in the technology industry offers valuable lessons for both established businesses and aspiring entrepreneurs. His perspective brings together technology, business strategy, and leadership, making the conversation relevant beyond just the IT industry. For young founders, business leaders, and technology professionals, his story can serve as a reminder that building a company is about much more than developing technology. It is about understanding people, solving meaningful problems, building trust and continuously adapting to change. Read the Full Interview With Subir Sangal The Sugermint interview goes deeper into Subir Sangal’s entrepreneurial journey, his views on the technology industry and the challenges businesses face in an increasingly digital world. Rather than focusing only on achievements, the conversation explores the thinking and experiences behind his approach to technology and business. If you are an entrepreneur, technology professional, business leader, or someone interested in India’s evolving technology ecosystem, the interview offers an engaging look at the lessons that come from years of experience. It is especially relevant for those trying to understand how technology businesses can remain competitive while navigating constant change. Frequently Asked Questions Why is cybersecurity important for businesses? + Cybersecurity helps businesses protect sensitive data, prevent cyberattacks, reduce financial losses, and maintain customer trust. It is essential for ensuring business continuity in an increasingly digital environment. What are the most common cybersecurity threats businesses face? + Common cybersecurity threats include phishing, ransomware, malware, data breaches, password attacks, and social engineering. These threats can disrupt operations, compromise sensitive information, and cause financial damage. How can small and medium-sized businesses improve their cybersecurity? + Small and medium-sized businesses can strengthen cybersecurity by implementing multi-factor authentication, regularly updating software, conducting employee awareness training, maintaining data backups, and using endpoint protection and network monitoring solutions. What is AI-driven 24×7 SOC monitoring, and how does it help businesses? + AI-driven 24×7 Security Operations Center (SOC) monitoring uses artificial intelligence to analyze security alerts, identify suspicious activities, and detect potential threats around the clock. It helps security teams prioritize risks, investigate incidents faster, and respond more effectively to cyber threats. How can businesses protect themselves from
Automotive Cybersecurity: Securing the Software-Defined Vehicle
Modern vehicles are rapidly transforming into software-defined machines driven by advanced connectivity and electronic control units. In this expert breakdown, Subir Sangal, CEO of Eagle, examines the critical security challenges facing the automotive industry—from expanding attack surfaces and third-party supply chain risks to over-the-air (OTA) update vulnerabilities and connected data protection. Learn why cybersecurity must evolve as an ongoing lifecycle commitment rather than a one-time factory test.
Synology Presents The Data Intelligence Dialogue
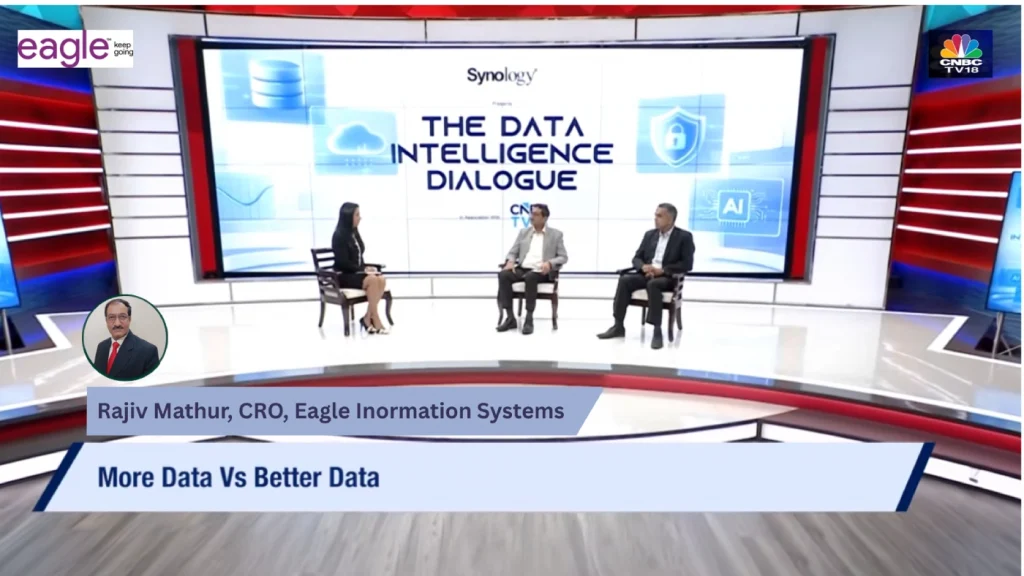
The rapid rise of Artificial Intelligence is reshaping the global data ecosystem, making data readiness, security, governance, and digital sovereignty more critical than ever. As enterprises scale their AI initiatives, the ability to securely manage and control data is becoming a key differentiator. In The Data Intelligence Dialogue, presented by Synology in association with CNBC-TV18, Rajiv Mathur, Chief Revenue Officer, Eagle, shares his perspectives on the evolving data landscape and the challenges organizations face in preparing for an AI-driven future. The AI Data Dilemma: Readiness, Control & the Rise of Digital Sovereignty The discussion explores whether enterprises have the right infrastructure, cybersecurity frameworks, and governance models to support AI at scale. From resilient storage architecture and cybersecurity to sovereign data ecosystems and private AI environments, the conversation highlights the growing need for organizations to take a strategic approach to their data. As AI continues to evolve, its success will depend not only on innovation but also on the strength of the data foundation supporting it. Secure, intelligent, and strategic data management will be at the heart of the AI-powered enterprise. Watch the full conversation with Rajiv Mathur and discover the key insights shaping the future of data intelligence, AI readiness, and digital sovereignty.
The AI Data Dilemma: Why Enterprises Are Rethinking Control, Sovereignty, and Infrastructure
Artificial Intelligence is transforming how enterprises operate, innovate, and compete. From intelligent automation and analytics to generative AI and industry-specific applications, businesses are generating and processing more data than ever before. As AI adoption accelerates, this raises an important question: Who controls the data that powers your AI? This was one of the key themes explored during Synology’s Data Intelligence Dialogue, presented in association with CNBC-TV18. The discussion brought together industry leaders Joanne Weng, Director of International Business, Synology Inc.; Brajesh Shrivastava, Director, Deduce Technologies; and Rajiv Mathur, Director, Eagle, to discuss how enterprises can build secure, resilient, and future-ready data infrastructure in the AI era. For Rajiv Mathur of Eagle, the conversation goes beyond technology. As enterprises adopt AI and manage growing volumes of critical data, security, governance, and control must become fundamental business priorities. Ensuring that data remains protected, accessible, and under the right level of control is essential for building a secure and future-ready AI strategy. AI Is Only as Strong as the Data Behind It AI models may be powerful, but their success depends on the quality, accessibility, and security of the data behind them. Today, enterprise data is spread across applications, endpoints, servers, databases, cloud platforms, and other environments. Without proper visibility and governance, this fragmented data can create security risks and make it difficult for organizations to get the right value from their AI investments. As AI adoption grows, businesses need to rethink their approach to data infrastructure. The question is no longer simply “Where should we store our data?” Instead, organizations need to understand where their data resides, who can access it, how it is protected, and how quickly it can be recovered when required. They also need to determine which data should remain on-premises, which can move to the cloud, and whether their infrastructure provides the necessary visibility, control, and compliance. These considerations are becoming even more important as AI systems increasingly interact with sensitive business and customer data. A future-ready AI strategy therefore requires more than computing power and storage—it requires a strong foundation of security governance, accessibility, and control to ensure that data remains protected while supporting innovation. Rajiv Mathur: Security Must Come First During the Data Intelligence Dialogue, Rajiv Mathur highlighted a point that is becoming increasingly important for businesses adopting AI: “Security of data is paramount. Whether we are compliant or not, security is going to be a very important chapter.” His message reflects a fundamental shift in how enterprises need to approach data as AI becomes a larger part of everyday business operations. While compliance remains important, it cannot by itself protect an organization from every threat. Businesses need to make security an integral part of how data is stored, accessed, managed, monitored, and backed up. With enterprise data growing in both volume and value, organizations must have the right safeguards in place to reduce risks and maintain control over their critical information. A security incident involving sensitive business or customer data can have consequences far beyond the IT department. It can disrupt business continuity, affect customer trust, and damage an organization’s reputation and operations. For businesses investing in AI, protecting the data that powers these investments must be just as important as the technology itself. The Cloud Is Not the Only Answer Cloud computing has played a major role in digital transformation by offering businesses flexibility, scalability, and access to powerful computing resources. However, as organizations manage increasing volumes of data, many are now taking a more balanced approach. Sensitive information may require greater control, regulatory requirements can influence where data is stored, and growing data volumes can also increase concerns around long-term infrastructure and operational costs. This is driving greater interest in hybrid infrastructure, where businesses can benefit from the flexibility of the cloud while retaining greater control over critical data on-premises. During the Data Intelligence Dialogue, Rajiv Mathur highlighted the importance of this approach, with organizations increasingly evaluating their data based on its sensitivity, business value, security requirements, and operational needs. Rather than putting all data into a single environment, businesses can decide where each type of data belongs. Critical or sensitive information can remain within controlled on-premises environments, while other workloads can leverage the cloud where it makes business sense. This approach allows organizations to achieve the right balance between flexibility, security, cost, and control as they prepare their infrastructure for the growing demands of AI. Data Sovereignty Is Becoming a Business Issue Data sovereignty is no longer just a regulatory or compliance concern; it is becoming an important business and security priority. As governments introduce stronger data protection and localization requirements, organizations need greater clarity over where their data is stored, processed, and managed. Maintaining control over critical data is increasingly important for businesses looking to reduce risk and build long-term resilience. For enterprises in India, this becomes particularly relevant as the country develops its own AI ecosystem and focuses on secure, locally relevant AI capabilities. Regional language models, industry-specific AI applications, and sensitive datasets require infrastructure that can support innovation while providing the right level of security, governance, and control. Ultimately, organizations need to know where their data is, who can access it, and how it is protected throughout its lifecycle. Having this visibility and control helps businesses strengthen security, meet evolving requirements, and build a resilient data infrastructure that is ready for the growing demands of AI. The New Priority: Control Your Data The AI era is changing how organizations think about data infrastructure. While storage capacity remains important, it is only one part of the bigger picture. A future-ready environment needs to bring together data, security, governance, backup, accessibility, and control to ensure that businesses can manage their growing data securely and efficiently. For enterprises, the focus must now move beyond simply storing and managing data to actively governing, protecting, and controlling it. This means having clear visibility into where data resides, who can access it, how it is protected, and how quickly
Cybersecurity Is the New Clinical Safety: Subir Sangal on Protecting the Future of Healthcare
Healthcare is becoming more connected, digital, and AI-driven. From hospital information systems and cloud platforms to connected medical devices and real-time patient monitoring, technology is now deeply integrated into patient care. However, with greater connectivity comes greater risk, making cybersecurity an increasingly important part of healthcare. A cyberattack on a hospital is no longer only an IT problem—it can become a patient safety problem. A disruption to critical systems, patient records, or connected medical technologies can impact clinical operations and the continuity of care. This makes protecting healthcare infrastructure essential not only for data security but also for patient safety and trust. This is the key message shared by Subir Sangal, CEO, Eagle, in his latest interaction with elets. In the feature, “Cybersecurity is the New Clinical Safety,” he explains why healthcare organizations must treat cybersecurity as an essential part of clinical safety, operational continuity, and patient trust. “Cybersecurity is not purely an internal IT responsibility.” Subir Sangal highlights a critical reality: hospitals operate 24×7, and so do cyber threats. In a connected healthcare environment, even a disruption to a patient monitoring system, emergency alarm, or critical care equipment can potentially affect patient care. Cybersecurity, therefore, goes far beyond protecting computers and data—it is about protecting the continuity and safety of healthcare services. He emphasises that hospitals need a strong, continuous security approach that includes 24×7 Security Operations Center (SOC) monitoring, strong data protection, complete visibility across IT environments, regular software health checks, appropriate access controls, and clear backup and recovery plans. Employee awareness and regular cybersecurity training are equally important in reducing human-related risks. The message is simple: you cannot protect what you cannot see, and you cannot wait for an attack to start protecting your hospital. Healthcare organizations need continuous monitoring, proactive security, and a resilient infrastructure to ensure technology remains an enabler of safe, uninterrupted patient care. AI Can Transform Healthcare—But Security Must Come First AI is opening new possibilities in healthcare, from predictive analytics and clinical decision support to smarter hospital operations. Subir Sangal believes AI should simplify healthcare, not complicate it. As hospitals increasingly adopt AI-driven technologies, ensuring that these systems are secure and reliable becomes equally important. As AI becomes more connected to patient data and critical hospital systems, any compromise or manipulation of information can have serious consequences. Incorrect or altered data could potentially influence clinical decisions and, ultimately, impact patient care. This makes cybersecurity an essential part of responsible AI adoption in healthcare. That is why AI adoption must go hand in hand with strong cybersecurity, patient privacy, network visibility, and appropriate human oversight. For Subir, the goal is clear: use technology and AI to make healthcare smarter and more efficient, while ensuring that security and patient safety remain at the center of digital transformation. Hospitals Cannot Afford Downtime Another important point Subir raises is operational continuity. Hospitals operate around the clock, and their critical systems cannot afford unexpected downtime due to a system failure, cyberattack, software update, or infrastructure issue. Technology must remain reliable and available when healthcare teams need it most. Billing systems, Hospital Information Systems (HIS), patient records, and connected technologies all play an important role in daily hospital operations. Any disruption can affect workflows and delay critical processes, taking attention away from what matters most: patient care. This is where managed IT services and a trusted technology partner can make a difference. By taking care of infrastructure, cybersecurity, legacy systems, compliance, and ongoing support, the right technology partner can help healthcare organizations build resilient IT environments that keep operations running smoothly and securely. Building Trust Through Secure Digital Healthcare As healthcare organizations increasingly embrace cloud, AI, and digital transformation, data governance and patient privacy are becoming more important than ever. With sensitive patient information moving across multiple systems and platforms, healthcare providers need to ensure that this data remains secure, accessible, and protected. Subir stresses that cybersecurity should not be treated as an additional layer added after digital transformation—it needs to be built into the transformation itself. For hospitals, this means combining secure technology with continuous monitoring, strong governance, seamless integration, and long-term ownership of their IT and security environments. Ultimately, healthcare technology has one clear purpose: to support doctors, protect patients, and keep care moving without interruption. By making cybersecurity an integral part of digital healthcare, organizations can build greater resilience, strengthen patient trust, and confidently embrace new technologies.
Enterprise AI Cybersecurity: Why Trust, Governance and Security Matter
Artificial intelligence is rapidly becoming part of how modern businesses operate. From automating processes and analysing information to supporting employees and improving decision-making, Enterprise AI is creating new opportunities for organisations across industries. But as AI becomes more deeply integrated into business operations, another question becomes increasingly important: How do you make sure AI remains secure, trusted and aligned with your business? As Eagle CEO Subir Sangal highlighted in a recent TechCircle discussion, the next phase of Enterprise AI will be shaped not simply by bigger models, but by trust, governance and security. The growth of AI also brings new cybersecurity risks, making security an essential part of every organisation’s AI strategy. Why AI Security Matters for Enterprises AI systems can interact with business applications, employee information, customer data and other sensitive resources. As organisations connect AI tools with their existing technology environments, the potential impact of a security incident can also increase. Businesses therefore need to consider cybersecurity at every stage of AI adoption. Protecting data, controlling access, monitoring activity and identifying vulnerabilities are all important to ensuring that AI delivers value without creating unnecessary cybersecurity risks. This makes AI cybersecurity more than a technology issue. It is a business requirement that should be considered alongside digital transformation, risk management and business continuity. Trust Must Be at the Centre of Enterprise AI For businesses to adopt AI confidently, they need to know that their information and systems are protected. Trust depends on having appropriate controls over who can access information, how data is used and how unusual activity is identified. Strong identity and access management, data protection and continuous monitoring can help organisations control access to sensitive systems and information. Businesses should also regularly assess their technology environments to identify weaknesses before they can be exploited. A secure approach to AI allows organisations to pursue innovation while keeping security and business priorities in focus. Governance and Cybersecurity Go Hand in Hand As AI becomes part of everyday business processes, organisations need clear rules around how it is used. Employees should understand what information can be shared with AI tools, how sensitive data should be handled and how suspicious activity should be reported. At the same time, technology teams need visibility into the systems supporting AI applications. Cybersecurity monitoring, vulnerability assessments, endpoint security, network security and data protection can help businesses identify and manage risks across their IT environment. Security should therefore not be treated as something added after an AI solution is deployed. It needs to be considered from the beginning. Protecting Enterprise AI Starts with Strong Cybersecurity Eagle’s cybersecurity services are designed to help businesses protect their systems, data and operations against evolving cyber threats. The portfolio includes risk assessment and advisory, infrastructure and network security, identity and access management, detection and monitoring, incident response and recovery, and human-centric security. Eagle also provides protection across key areas including threat detection and prevention, endpoint security, network security, data encryption and protection, vulnerability assessment and penetration testing (VAPT), and incident response and recovery. For organisations looking to identify weaknesses before attackers can exploit them, Eagle’s VAPT services cover network infrastructure, servers and endpoints, web applications and APIs, and cloud and hybrid environments. The approach combines automated tools, expert analysis and real-world attack techniques, followed by risk analysis and remediation guidance. 24/7 Security Monitoring for a Changing Threat Landscape AI-driven businesses need security that operates continuously. Cyber threats do not stop outside business hours, and organisations need visibility into potential threats across their environments. Eagle’s 24/7 Security Operations Center (SOC) provides continuous monitoring, proactive risk management and rapid issue resolution. Its SOC uses technologies including SIEM, EDR and XDR, supported by L1, L2 and L3 capabilities. Continuous security monitoring can help organisations detect threats earlier, investigate suspicious activity and respond quickly when security incidents occur. Securing AI Without Slowing Innovation The goal of cybersecurity is not to prevent businesses from adopting new technologies. It is to help them adopt those technologies with greater confidence. As organisations introduce AI into applications, workflows and decision-making, security needs to evolve alongside that transformation. A strong cybersecurity strategy can help businesses protect sensitive information, manage access, identify vulnerabilities and respond to threats while continuing to innovate. This is where trust, governance and security become critical to the future of Enterprise AI. Build a More Secure AI-Ready Business with Eagle Enterprise AI can deliver significant business value, but that value depends on how securely it is implemented and managed. Organisations that build security into their AI strategy can be better positioned to innovate while protecting the systems, information and people that matter most. Eagle helps businesses strengthen their cybersecurity posture through 24/7 SOC monitoring, threat detection, endpoint security, network security, data protection, identity and access management, VAPT, and incident response and recovery. With more than three decades of experience delivering IT and BPO services, Eagle supports organisations across industries with scalable technology and cybersecurity solutions. Building smarter AI starts with protecting what matters most. Strengthen Your Cybersecurity.
As Enterprise Learning Turns AI-Native, Workday Shifts from Compliance to Outcomes
Enterprise learning is entering a new phase. As artificial intelligence becomes embedded in workplace learning, organisations are moving beyond traditional compliance-focused training toward continuous skill development, measurable outcomes and business impact. The shift reflects a broader change in how enterprises approach technology. AI-powered learning platforms can help organisations identify skill gaps, personalise learning journeys and make workforce development more closely aligned with business priorities. Subir Sangal, CEO of Eagle Information Systems, shares his perspective on the evolution of AI-powered enterprise learning and why organisations need to build a workforce that is agile, skilled and prepared for an increasingly AI-driven business environment. From Compliance Training to Business Outcomes For years, enterprise learning programmes have been measured largely through course completion rates, certifications and compliance requirements. While these metrics remain important, they do not always show whether employees have developed skills that contribute to improved business performance. AI is changing this approach. AI-native learning can analyse employee roles, existing skills, learning behaviour and business requirements to create more personalised development paths. Instead of focusing only on whether an employee completed a course, organisations can assess whether learning improved productivity, strengthened capabilities or helped employees prepare for emerging technologies. This outcome-driven approach is particularly valuable in IT environments, where technologies, cybersecurity threats and business requirements are constantly evolving. By aligning learning with real business needs, organisations can build a more skilled, adaptable and future-ready workforce. Why Continuous Learning Matters for Cybersecurity For years, enterprise learning programmes have been measured largely through course completion rates, certifications and compliance requirements. While these metrics remain important, they do not always demonstrate whether employees have developed the skills needed to improve business performance. AI is changing this approach. AI-native learning can analyse employee roles, existing skills, learning behaviour and business requirements to create more personalised development paths. Instead of focusing only on course completion, organisations can evaluate whether learning has improved productivity, strengthened capabilities and prepared employees for emerging technologies. This outcome-driven approach is particularly valuable in IT environments, where technologies, cybersecurity threats and business requirements are constantly evolving. By aligning learning with real business needs, organisations can build a more skilled, adaptable and future-ready workforce. AI Makes Cybersecurity Awareness More Relevant Traditional cybersecurity awareness training can be less effective when employees receive the same generic content, regardless of their roles or the risks they face in their daily work. Different employees interact with different types of information and technology, so their security training should reflect those responsibilities. AI can help make cybersecurity learning more relevant to individual roles. Employees who handle customer information can receive greater focus on protecting sensitive data, while IT teams can learn more about securing systems, managing access and identifying potential threats. Security teams can also receive regular updates on new cyber threats and ways to respond to them. The goal is not simply to increase the number of training hours or courses completed. It is to help employees understand security risks, make safer decisions and respond appropriately to potential threats, creating a stronger and more secure organisation. The Connection Between Skills, AI and Cyber Resilience As businesses adopt AI, cloud platforms and increasingly connected IT environments, cybersecurity is becoming more complex. Employees need to understand not only how to use new technologies effectively but also how to use them safely and responsibly. A future-ready workforce should have a strong understanding of Cybersecurity awareness and phishing prevention, Identity and access management, and Data privacy and protection. Employees should also be trained in the Secure use of cloud and AI technologies, Endpoint and network security, and Incident reporting and response so they can recognise risks and respond appropriately. Organisations should also focus on Compliance and security best practices as part of ongoing employee learning. By connecting learning with broader technology and cybersecurity strategies, businesses can help employees develop safer working practices while staying prepared for evolving technologies and cyber threats. Continuous Learning Needs Continuous Cybersecurity As learning platforms become more intelligent, the systems supporting them also need to be protected. Enterprise learning environments can contain sensitive employee information, organisational data, credentials and potentially proprietary content. Organisations therefore need appropriate controls around identity, access, data protection and monitoring. Eagle’s cybersecurity services include data encryption and protection, endpoint security, network security, threat detection and prevention, vulnerability assessment and penetration testing, and incident response and recovery. Its 24/7 SOC capabilities use technologies such as SIEM, EDR and XDR for continuous security monitoring. This is particularly relevant as enterprises expand their use of AI-enabled applications and cloud-based platforms. Security needs to evolve alongside digital transformation to help organisations protect their information and maintain a secure technology environment. Moving from Learning Activity to Measurable Impact The larger lesson from the AI-native learning shift is that technology should ultimately create measurable business value. For enterprise leaders, the focus is moving beyond training completion to understanding how learning contributes to business performance and long-term growth. Enterprise leaders need to ask whether employees are developing the skills the business needs, whether those skills are improving operational performance, and whether employees are better prepared to identify and respond to cybersecurity threats. They also need to consider whether the organisation can continuously adapt as technologies and risks change. These questions move enterprise learning from a compliance exercise toward a strategic capability. By connecting learning with business goals, operational performance and cybersecurity, organisations can build a more skilled, adaptable and future-ready workforce. Building a Future-Ready and Cyber-Resilient Workforce AI can help organisations personalise learning and identify emerging skill requirements, but technology alone cannot create a secure enterprise. Businesses also need strong cybersecurity foundations, continuous monitoring and proactive risk management. Eagle helps enterprises strengthen these foundations through comprehensive cybersecurity services covering threat detection, endpoint security, network security, data protection, VAPT, incident response and recovery, identity and access management, and 24/7 SOC monitoring. Eagle’s broader IT services also span managed services, network management, professional services, data storage and cybersecurity, supporting organisations as they modernise their technology environments.
Bank of Baroda Data Breach: 5 Things Every Account Holder Should Know
The reported Bank of Baroda data leak has brought renewed attention to a critical cybersecurity challenge: protecting sensitive customer and business data in an increasingly connected environment. Reports in July 2026 indicated that a large volume of Bank of Baroda customer and internal data had surfaced online. The bank said the incident involved the compromise of an employee email account and stated that its core banking systems had not been accessed and remained secure. For customers, this distinction is important. A data breach does not automatically mean that bank accounts have been compromised or that money can be withdrawn. However, exposed personal information can create opportunities for phishing, identity theft, social engineering and account takeover attempts. As Subir Sangal, Chief Executive at Eagle Information Systems, noted in his comments to India Today Tech, if leaked information can be used for identity verification or account recovery, there is a potential risk of unauthorised access. He recommended changing passwords, enabling multi-factor authentication where available and closely monitoring account activity. What Happened in the Bank of Baroda Data Leak? Reports indicated that hundreds of gigabytes of Bank of Baroda-related information, potentially including customer details, identification documents, loan-related records and internal documents, appeared online. Bank of Baroda attributed the incident to unauthorised access following the compromise of an employee email account and stated that its core banking systems were not accessed. The complete scope of affected data and customers continues to be assessed. The incident highlights why cybersecurity cannot focus only on core applications. Email accounts, file-sharing platforms, endpoints, identities and employee access can all become potential entry points for cyber attackers. 5 Things Bank of Baroda Account Holders Should Know 1. A data leak does not necessarily mean your bank account has been hacked The reported incident does not indicate that Bank of Baroda’s core banking systems were accessed. Therefore, customers should not assume that their bank balance or transactions are automatically at risk. However, exposed personal information can still be valuable to cybercriminals. Details such as names, identification information, account-related data and other personal records could potentially be used to make fraudulent communications appear legitimate. This is why identity and access management, multi-factor authentication and continuous security monitoring are important components of a modern cybersecurity strategy, helping organisations strengthen protection against unauthorised access and evolving cyber threats. 2. The biggest immediate risk may be phishing and social engineering When attackers obtain legitimate-looking customer information, they can use it to create highly convincing phishing scams and social engineering attacks. Familiar details can make fraudulent messages appear genuine and increase the likelihood of customers responding to them. Customers may receive messages claiming that their account has been blocked, their KYC needs to be updated, or immediate action is required following the data breach. Such messages may be designed to trick users into sharing passwords, OTPs, banking credentials or other sensitive information. Customers should therefore avoid clicking links in unexpected SMS messages, emails or WhatsApp communications. Instead, they should access banking services only through the official app or website and verify any suspicious requests directly with the bank. 3. Change passwords and strengthen authentication As a precaution, customers should review their banking credentials and change passwords where appropriate. Passwords should be unique and should not be reused across banking, email and other online accounts. Where available, multi-factor authentication (MFA) adds another layer of protection by requiring an additional verification factor beyond a password. From an enterprise cybersecurity perspective, this principle extends across the organisation. Strong identity controls, least-privilege access and continuous authentication can significantly reduce the impact of compromised credentials. 4. Monitor transactions, alerts and credit activity Vigilance is particularly important following a data breach, as exposed information may be used in attempts to target customers through fraud or social engineering. Staying alert can help identify suspicious activity before it escalates. Customers should regularly review their bank statements and transaction alerts and report anything unusual immediately. They should also be cautious about unexpected OTP requests, unfamiliar calls from people claiming to represent the bank, or requests for additional personal information. Since exposed identity information can potentially be misused beyond banking, monitoring credit activity can provide an additional layer of protection. Identifying unfamiliar accounts, transactions or credit enquiries early can help customers take timely action. 5. Businesses need to look beyond the perimeter The Bank of Baroda incident also offers an important lesson for organisations: cybersecurity is not simply about protecting a firewall or a data centre. A compromised employee account can potentially provide a pathway to sensitive information. This makes email security, endpoint protection, identity management, employee awareness, vulnerability management, data protection and security monitoring essential parts of an organisation’s overall security posture. For enterprises handling customer, financial, healthcare or other sensitive information, proactive cybersecurity measures can help identify weaknesses before attackers exploit them. What Businesses Can Learn From the Bank of Baroda Data Breach The incident reinforces several cybersecurity priorities for modern enterprises: Identity & Access Management: Restrict access to sensitive systems and information based on business need, while strengthening authentication controls. Threat Detection & Monitoring: Continuous monitoring can help security teams identify suspicious behaviour and respond to threats before they escalate. Vulnerability Assessment & Penetration Testing: Regular VAPT can uncover exploitable weaknesses across infrastructure and applications before attackers find them. Data Protection: Sensitive information should be protected through appropriate access controls, encryption and security policies. Incident Response & Recovery: Organisations need clearly defined processes to contain incidents, investigate their impact and restore normal operations quickly. Human-Centric Security: Employees remain a critical part of the security equation. Security awareness, phishing preparedness and appropriate access controls can reduce the likelihood and impact of account compromise. Building a Stronger Cybersecurity Strategy At Eagle Information Systems, cybersecurity is approached as a comprehensive business requirement rather than a single technology deployment. Eagle’s cybersecurity services cover incident handling and investigation, data loss prevention, proactive risk & exposure management, threat intelligence & advanced detection, and governance, compliance & the human layer. Eagle also provides 24/7 Security Operations Center (SOC)