Eagle

Cybersecurity Services - Shield your business.

24×7 SOC Monitoring for a safer tomorrow.

Shielding your business today.

For a safer tomorrow.

One cyberattack can stop your business. Our AI-powered 24×7 Security Operations Center and experts provide rapid responses to protect you around the clock. We detect threats early and act before they spread. We provide enterprise-grade security without the need to build a security team at affordable and customized prices. We provide global service support.

Cyber attacks are not just IT glitches but full-scale business disruptions that demand proactive, resilient security to safeguard your operations. Read more

24x7 Protection and Efficiency

Security Operations Center

Our SOC provides continuous monitoring for maximum network uptime and rapid issue resolution. With proactive risk management and L1, L2, and L3 support, we secure your network using advanced SIEM, SOAR, EDR, XDR, and top cybersecurity tools—customized to fit your business needs.

Our Services

icon
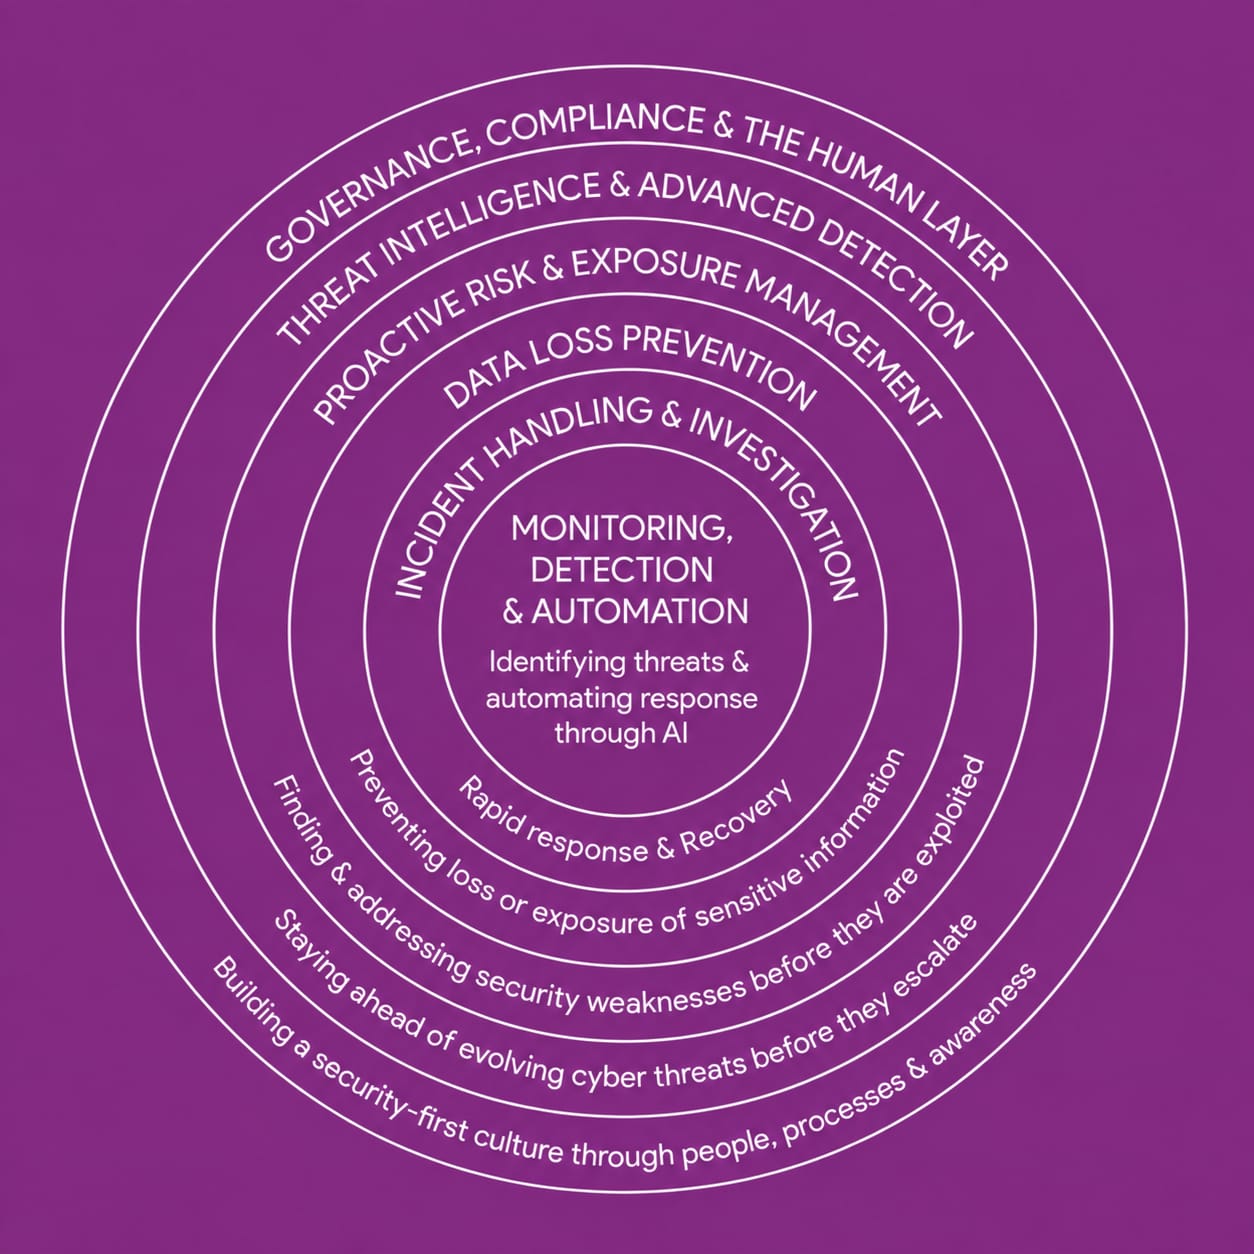
Monitoring, Detection & Automation
Our 24/7 SOC uses SIEM and SOAR for continuous visibility and rapid, automated threat response across network, cloud, and identity systems. Read More
icon
Incident handling and investigation
Our Incident Response Retainer and Digital Forensics deliver immediate action to neutralize threats, find root causes, and restore operations safely. Read More
icon
Data loss prevention
Our Data Loss Prevention (DLP) strategy tracks, classifies, and protects sensitive information across endpoints, cloud, and email to prevent leaks. Read More
icon
Proactive risk & exposure management
We do regular VAPT (Vulnerability Assessment & Penetration Testing) and patch management to close security gaps, shrinking your attack surface so that small flaws don’t become big breaches. Read More
icon
Threat intelligence & advanced detection
Proactive threat hunting and threat intelligence uncover hidden risks early. This empowers your team to strengthen endpoint security with Endpoint Detection & Response (EDR), enhance ransomware protection, block covert attacks, and minimize business loss. Read More
icon
Governance, compliance & the human layer
ISO 27001 governance, combined with employee security awareness and phishing training, reduces human error, ensuring full compliance and a strong safety culture. We also help organisations address data protection requirements under the DPDP Act and support their journey towards DPDP Complaince. Read More
Core Methodology

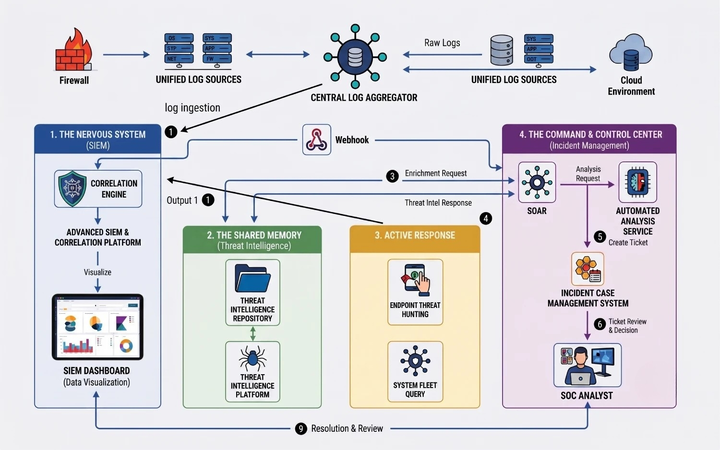
Our cybersecurity framework is designed to deliver end-to-end visibility and coordinated response across your entire environment. From threat detection to analysis, response and investigation – this workflow brings together multiple security layers into a single, streamlined process. Each component works in sync to ensure threats are identified early, analysed accurately, and acted upon quickly.

Our Portfolio

Our unified cybersecurity system brings all your security tools together into one easy workflow. It continuously checks, detects, and quickly stops threats, keeping your entire digital setup safe from attacks. Read More

Data Privacy Compliance Advisory

At Eagle, we help organizations strengthen their digital data compliance readiness with advisory services aligned with the DPDPA, GDPR, PDPA, LGDP, CCPA, and other applicable privacy frameworks. Read More

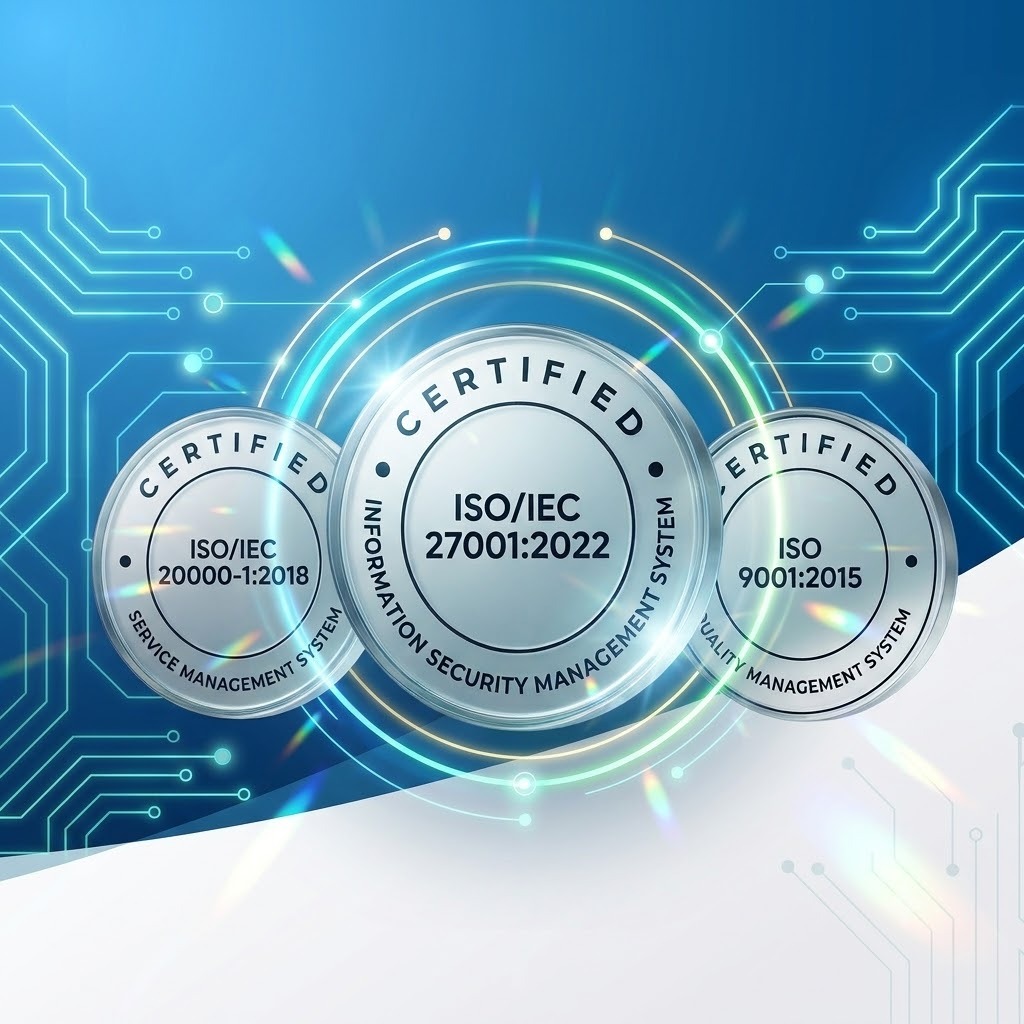
Built on ISO Standards

Eagle is ISO 9001:2015, ISO/IEC 20000-1:2018, and ISO/IEC 27001:2022 compliant to deliver proactive, resilient cybersecurity you can trust. Our internationally recognized certifications reflect an unwavering commitment to operational excellence, seamless IT service management, and robust data protection.

Multi Tiered Defense Framework

Powered by Eagle’s AI-enabled SOC, our connected security strategy delivers continuous monitoring and intelligent analysis to swiftly catch, contain, and neutralize evolving cyber threats before they disrupt your business. Read More

Eagle Advantage

At Eagle, we combine human expertise with AI-driven capabilities to deliver smarter, faster, and more accurate security outcomes. Our approach goes beyond isolated tools—bringing intelligence, automation, and expert decision-making together.

At the core of this is Eagle’s Security Operations Center (SOC), where AI-assisted monitoring and expert analysis work together to detect threats early and respond in real time. Read More

Frequently Asked Questions (FAQs)

Do we need to replace our existing security tools?

Not at all! We start by reviewing what you already use, such as firewalls, endpoint protection, email security, and cloud tools, and connect them to our SOC so alerts are monitored around the clock.

We recommend changes only when we identify a real gap, such as missing endpoint detection and response (EDR) or limited log visibility. You can continue using the tools you have already invested in.

How is the service priced?

Pricing is tailored to your environment, as every business has different numbers of users, devices, servers, and log sources, along with different coverage needs.

You choose the services you need, such as 24x7 SOC monitoring, VAPT, data loss prevention, or an incident response retainer. We provide a quote based on those requirements.

After a short scoping call, you receive a clear written proposal with no hidden costs.

Can you help with DPDP Act compliance?

Yes. We help organizations understand and address their data protection requirements under India's Digital Personal Data Protection (DPDP) Act and support their compliance efforts.

This includes assessing where personal data is stored, strengthening the security controls that protect it, and training employees to reduce human error. We can also advise on other privacy frameworks, such as GDPR, if your organization handles international data.

What happens if there is an incident?

Our SOC analysts act promptly, so you are not left to manage the incident alone.

  • Detect and triage: We confirm the threat and assess its severity.
  • Contain: We isolate affected systems to help prevent the threat from spreading, as agreed in your contract.
  • Investigate: Our digital forensics team investigates the root cause and identifies what was affected.
  • Recover: We help you restore operations safely and address the security gap.
  • Report: You receive a clear summary for management and, where required, your auditors.

With an incident response retainer, you also get priority access to our team.

Is this suitable for a small or mid-sized business?

Yes. This service is designed for small and mid-sized businesses that need enterprise-grade protection without hiring and managing their own 24x7 security team.

You get access to L1, L2, and L3 security analysts and proven security tools, with services tailored to your organization's size and budget.

You can start with essentials such as security monitoring and endpoint protection, then add services like VAPT or data loss prevention as your needs grow.

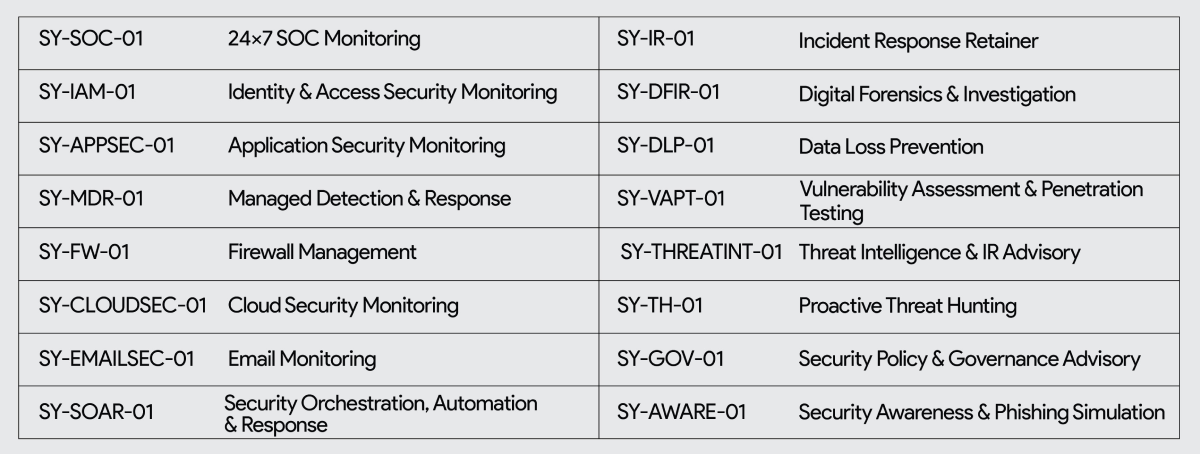
SY-SOC-01 24×7 SOC Monitoring
SY-DFIR-01 Digital Forensics & Investigation
SY-EDR-01 Endpoint Detection & Response
SY-DLP-01 Data Loss Prevention
SY-NETMON-01 Firewall, IDS/IPS Monitoring
SY-VAPT-01 Vulnerability Assessment & Penetration Testing (VAPT)
SY-EMAILMON-01 Email Monitoring
SY-PATCH-01 Patch Management
SY-APPSEC-01 Application & API Security Monitoring
SY-THREATINT-01 Threat Intelligence & IR Advisory
SY-IAM-01 Identity & Zero Trust Access Monitoring
SY-TH-01 Proactive Threat Hunting
SY-CLOUDSEC-01 Cloud Security Monitoring
SY-GOV-01 Security Policy & Governance Advisory
SY-IR-01 Incident Response Retainer
SY-AWARE-01 Security Awareness & Phishing Simulation