
Cybersecurity Resources
The Strategic Business Shield Every SME & Corporate Needs
Imagine running a high-volume manufacturing plant, a financial firm, or a sprawling retail enterprise. You have installed physical CCTV cameras, hired security guards at the main gates, and locked every entrance.
Now imagine this: at 2:00 AM on a long weekend, someone breaks through a basement window. The silent alarm trips, but nobody is actively monitoring the control panel. By Monday morning, your inventory is stolen, your records are tampered with, and operations are forced to shut down.
In today’s interconnected business ecosystem, this exact scenario plays out digitally every single day. Indian SMEs and mid-market corporates invest heavily in firewalls, cloud software, and antivirus tools. Yet, without continuous, active monitoring, hidden cyber threats blend right into daily network traffic—staying undetected until the damage is already done.
This operational gap is precisely why modern enterprises rely on a Security Operations Center (SOC).
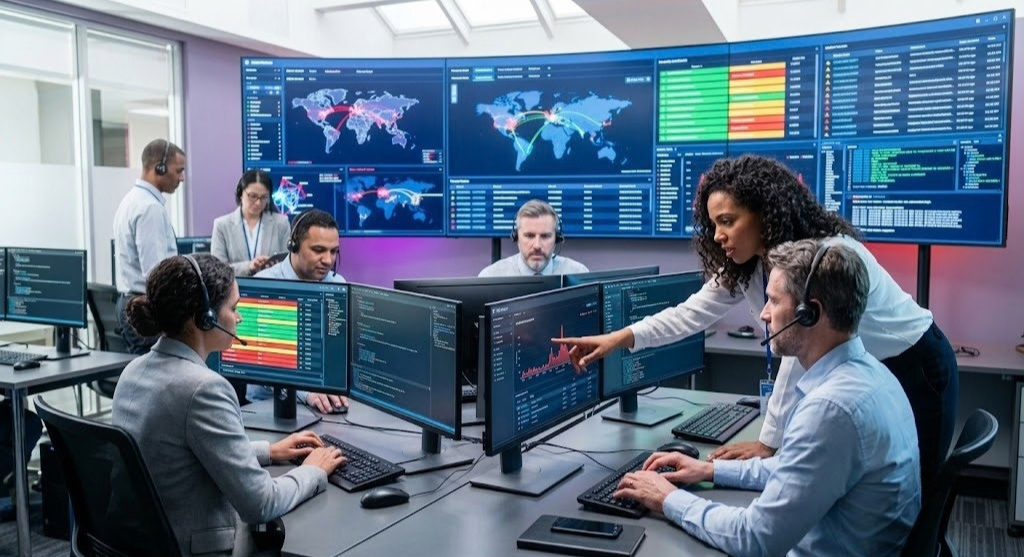
A Security Operations Center (SOC) is a centralized facility—powered by skilled cybersecurity engineers, structured processes, and AI-driven technology—that continuously monitors, detects, analyzes, and neutralizes cyber threats across an organization’s entire digital ecosystem, 24 hours a day, 7 days a week, 365 days a year.
Instead of relying on isolated security tools that create fragmented alerts, a modern SOC gives leadership total visibility across endpoints, cloud workloads, internal networks, emails, user identities, and third-party vendor integrations.
Why SMEs and Corporates Can No Longer Ignore SOC Monitoring
1. “We Are an SME—Why Would Hackers Target Us?”
Many Indian business owners assume cybercriminals only go after large banks or multi-billion-dollar conglomerates. The reality? Automated attack bots do not check your annual turnover. Hackers target SMEs because they often lack 24×7 defenses. SMEs are routinely targeted for customer databases, financial records, ransomware extortion, or as an entry vector into larger corporate supply chains.
2. Differentiating Compliance from Real Security
Meeting regulatory standards—such as CERT-In directives, the DPDP Act (Digital Personal Data Protection), ISO 27001, or RBI/SEBI guidelines—is mandatory. However, compliance is not an active defense. Having written security policies on paper will not stop an active ransomware attack at 3:00 AM on a Sunday. Continuous SOC monitoring bridges the gap between compliance on paper and real-world cyber resilience.
3. Preventing Full-Scale Business Disruption
A cyber incident is not just an IT inconvenience; it is a critical business risk. Unchecked breaches lead to operational downtime, reputational damage, legal liabilities, and heavy compliance penalties. A SOC ensures that a minor security flaw is contained before it turns into a business-ending disaster.
The Next Evolution: Why AI-Driven SOC is a Game Changer for Modern Enterprises
Traditional SOC setups often suffer from “alert fatigue,” where human analysts get overwhelmed by thousands of false alarms every day, causing critical threats to slip through the cracks. An AI-driven SOC transforms this dynamic by integrating machine learning models, predictive analytics, and automated playbooks directly into the threat detection pipeline. AI algorithms instantly filter out benign system noise, correlate complex threat patterns across cloud and endpoint environments in milliseconds, and execute rapid, automated responses before a breach can spread. By offloading routine data processing to AI, human security engineers can focus on deep threat hunting and strategic incident response—offering SMEs and corporates faster response times, lower operational costs, and proactive protection against zero-day cyberattacks.
How Does an Enterprise SOC Work?
A SOC acts as the command center for your digital defense. Rather than reacting after an outage, it follows a structured, proactive operational workflow:
- Continuous Data Aggregation: The SOC collects log data and event telemetry from across your environment—firewalls, laptops, servers, cloud setups (AWS, Azure, M365), and core applications.
- SIEM-Driven Correlation: Using Security Information and Event Management (SIEM) tools, millions of routine log events are analyzed in real time to spot hidden anomalies.
- Analyst Triage & Threat Hunting: Tier-1 to Tier-3 security analysts verify alerts, separating benign system glitches from genuine malicious intent to eliminate “alert fatigue”.
- SOAR-Driven Containment: Utilizing Security Orchestration, Automation & Response (SOAR), automated playbook actions—like isolating an infected laptop or blocking a malicious IP address—take place within seconds.
- Incident Response & Recovery: Digital Forensics and Incident Response (DFIR) specialists assess the root cause, close the security gap, and help restore normal operations with zero data loss.
Key Capabilities of a Connected Enterprise SOC
As outlined in the core methodology from Eagle Information Systems, an enterprise-ready SOC combines multiple layers of defense into a unified workflow:
Security Domain | What the SOC Monitors & Protects |
Endpoint Protection (EDR/XDR) | Detects, isolates, and neutralizes malware, ransomware, and suspicious execution on user devices. |
Cloud & Identity Security | Tracks unauthorized privilege access, misconfigurations, and identity theft in hybrid and multi-cloud environments. |
Network & Firewall Monitoring | Real-time monitoring of network traffic, IDS/IPS feeds, and perimeter access logs to block unauthorized intrusions. |
Email & Application Security | Flags sophisticated phishing campaigns, business email compromise (BEC), and API abuse. |
VAPT & Exposure Management | Conducts regular Vulnerability Assessment & Penetration Testing to find and patch entry points before attackers exploit them. |
Build vs. Buy: In-House SOC vs. Managed SOC (MSOC)
For most growing companies, building an internal 24×7 SOC from scratch is cost-prohibitive. It requires hiring specialized 24×7 shift teams, buying software licenses, and setting up redundant hardware.
Partnering with a trusted Managed Security Service Provider (MSSP) like Eagle Information Systems gives SMEs and enterprise teams access to AI-driven SOC capabilities, experienced Tier-1/2/3 security talent, and enterprise-grade tools—without the overhead of managing an in-house security team.
Strategic Takeaway for Business Leaders
In modern cybersecurity, the core question is no longer “Will our network be targeted?”—it is “How quickly can we detect, isolate, and eliminate a threat when it arrives?”
By combining AI-driven automation with human intelligence, a 24×7 SOC helps safeguard business continuity, protect customer trust, and allow your executive team to focus on business growth.
Frequently Asked Questions (FAQs)
1. What is the difference between an in-house SOC and a Managed SOC (MSOC)?
An in-house SOC is owned, operated, and staffed internally by a company, requiring significant capital investment in 24×7 security talent, SIEM software, and infrastructure. A Managed SOC (MSOC) is an outsourced security service provided by an MSSP (like Eagle Information Systems) that delivers 24×7 monitoring, threat detection, and incident response on a flexible subscription basis at a fraction of the cost.
2. Why do small and medium enterprises (SMEs) need a SOC in India?
SMEs in India need a SOC because modern cyberattacks—such as ransomware, phishing, and supply chain breaches—are automated and target businesses regardless of company size. A SOC helps SMEs meet regulatory compliance (like CERT-In directives and the DPDP Act), prevents expensive business downtime, and provides round-the-clock defense without needing an expensive internal security team.
3. How does artificial intelligence (AI) improve a Security Operations Center?
AI improves a SOC by processing millions of security logs in real time to filter out false alarms, reduce analyst fatigue, and detect hidden anomalies across endpoints and cloud networks. An AI-driven SOC uses machine learning and automated SOAR playbooks to isolate cyber threats within seconds, significantly reducing response times.
4. What primary tools and technologies are used in a modern SOC?
A modern enterprise SOC relies on a integrated stack of security tools, including:
- SIEM (Security Information and Event Management) for log correlation and centralized monitoring.
- SOAR (Security Orchestration, Automation and Response) for automated incident mitigation.
- EDR/XDR (Endpoint Detection and Response) for user device protection.
- VAPT (Vulnerability Assessment & Penetration Testing) for proactive threat discovery.
5. Is having a firewall and antivirus software enough without a SOC?
No. Firewalls and antivirus software act as initial security barriers, but they only block known, standard threats. They cannot actively hunt for sophisticated threats, detect unauthorized lateral movement inside your network, or monitor suspicious behavior after hours. A SOC provides the active, 24×7 human and AI surveillance needed to respond when perimeters are breached.